How to Use 1Password with the SyncBackPro Secrets Manager
If your organisation keeps its passwords in 1Password, SyncBackPro can take backup credentials from there instead of storing them in each profile. It can read the username and password of a 1Password item and use them in a profile, for example for an FTP server, a network share, a cloud account or an encrypted Zip file. The profile holds only a reference to the item, not the value. When a password changes, you change it once in 1Password and every profile that uses it picks up the new value on its next run.
The Secrets Manager is only available in SyncBackPro. It is not in SyncBackSE or SyncBackFree. Support for 1Password was added in SyncBackPro V12.
You need a 1Password Connect server
Unlike Bitwarden and Dashlane, SyncBackPro does not talk to 1Password directly. It talks to a 1Password Connect server that you run yourself, and that server talks to 1Password. So "setting up 1Password as a secrets manager" mostly means deploying a Connect server. 1Password service accounts, the 1Password SDKs, the 1Password CLI (op) and desktop app sign-in are not supported.
TL;DR
Create a new shared vault for your backup credentials. On 1Password.com create a Connect server with access to that vault, save its credentials file and create an access token. Run the Connect server in Docker on your own network. In SyncBackPro add a 1Password connection with the token, the server's URL and the vault ID, create secrets for the items, and pick them in your profiles with Use a secret. Only usernames and passwords can be used, and the token's expiry date is the thing most likely to catch you out.
Table of Contents
What you need
- A 1Password account that can use Secrets Automation. Connect servers are included at no extra cost, and not only on business plans: they also work with a 1Password Individual account. On a Teams or Business account, your 1Password user must be in a group with permission to manage Secrets Automation.
- A machine to run the Connect server, for example a Linux server, a NAS or a virtual machine, with Docker installed. It can, and usually should, be on your local network only. It does not need to be reachable from the Internet.
- Network access from the computer running SyncBackPro to that machine.
Setting up 1Password for SyncBackPro
1Password may change its menus at any time. The steps below were correct when this article was written, and the 1Password Connect documentation is the definitive source.
Step 1: Create a shared vault
A Connect server cannot access your Personal, Private or Employee vault, nor the default Shared vault. Create a new shared vault, for example SyncBack, and put in it only the logins and passwords that your backup profiles need.
Step 2: Create the Connect server and an access token
Sign in to your account on 1Password.com, then:
- Go to Developer, then Directory. Under Infrastructure Secrets Management choose Other, then Create a Connect server.
- Give the server a name and tick the shared vault from step 1. A Connect server can only see the vaults you tick here.
- Save the 1password-credentials.json file you are offered. This is how the Connect server itself signs in to 1Password, so keep it safe.
- Create an access token for the server and give it access to the same vault. You cannot change which vaults a token can see after you create it. Copy the token, as it is not shown again, and make a note of the expiry you choose: when the token expires, the profiles that use it stop working.
If you prefer the command line, the 1Password CLI can do the same with op connect server create and op connect token create.
Step 3: Deploy the Connect server
Copy 1password-credentials.json to the machine that will run the server, and put the docker-compose.yaml file that 1Password provides in the same folder. It starts two containers: 1password/connect-api, the REST API that SyncBackPro talks to, and 1password/connect-sync, which keeps the server's data in step with your 1Password account. Then start it:
docker compose up -dIf you use Kubernetes, 1Password also provides a Helm chart. By default the API listens on port 8080.
Step 4: Test it from the SyncBackPro computer
From the computer that will run SyncBackPro, request the list of vaults, passing the access token in the Authorization header. With curl, which is included with current versions of Windows, run this in a Command Prompt (in Windows PowerShell, type curl.exe instead of curl, because curl there is a different command):
curl -H "Authorization: Bearer <access token>" http://hostname:8080/v1/vaultsYou should get back a list of the vaults the token can see, each with an id and a name. If that works, SyncBackPro will work.
Step 5: Find the vault ID
SyncBackPro needs the vault ID, not the vault name. It is the id value in the response from step 4. You can also get it with op vault list in the 1Password CLI, or from the address bar when you open the vault on 1Password.com.
Creating the connection in SyncBackPro
- Run SyncBackPro, click the burger menu
 and choose Secrets Manager.
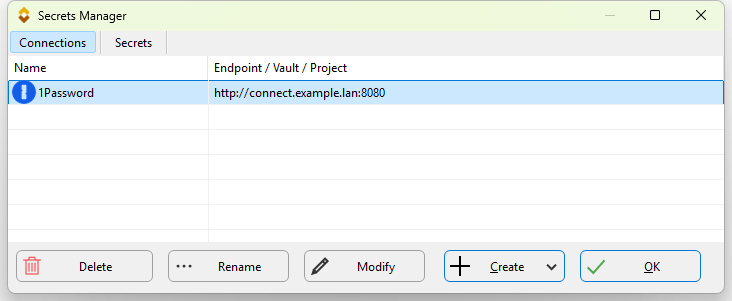
- On the Connections page, click Create and choose 1Password.
- You are asked for each of these in turn:
- Name: a name for the connection, for your own reference.
- URL: the address of your Connect server, for example http://hostname:8080. Do not include /v1, as SyncBackPro adds it itself.
- Vault Token: the access token from step 2.
- Vault: the vault ID from step 5.
SyncBackPro connects straight away and lists the items in the vault, so you find out immediately if anything is wrong.
Creating secrets and using them in a profile
A connection gives SyncBackPro access to the vault. A secret tells it which item, and which field of that item, to use. One connection can be used by many secrets, and one secret by many profiles.
- In the Secrets Manager, go to the Secrets page, click Create and choose Username or Password.
- If you have more than one connection, choose the 1Password one. Then pick the item by its Name (its title in 1Password) from the list that SyncBackPro reads from the vault, and click OK.
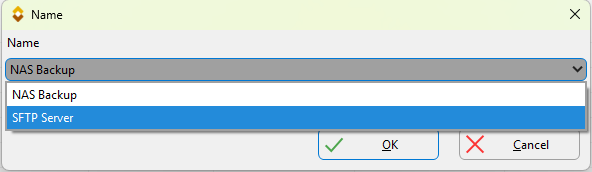
- A Description is filled in with the item's category, Login or Password. Change it if you like; it is for your own reference.
- If the item has both a username and a password, a Key dialog asks which one to use: username or password. If it has only one of them, that one is used without asking. Click OK.
- Now open the profile, either in the New Profile Wizard or with Modify. Beside a field that can take a secret, for example the FTP password, click the drop-down button and choose Use a secret. Pick the secret and click OK.
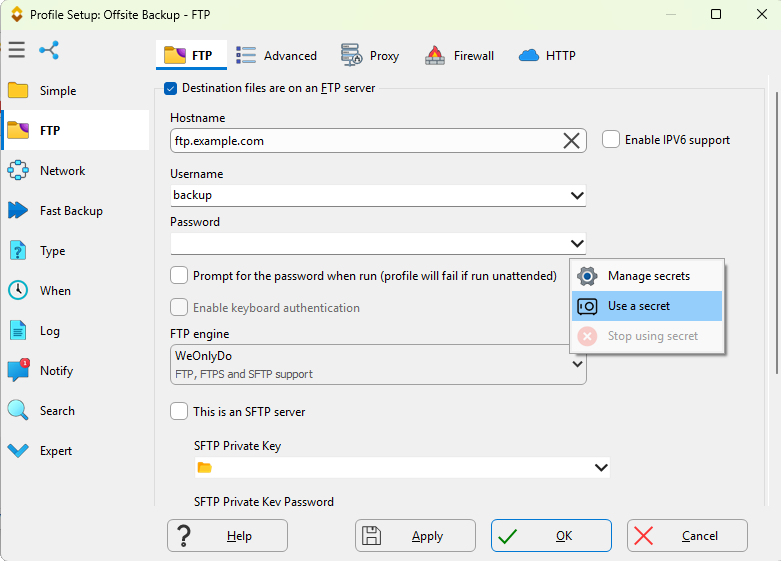
The hint on the drop-down button shows which secret the field is using. The same menu has Manage secrets and Stop using secret, and once a secret is in use, Use a secret becomes Change secret, followed by the name of the secret.
A 1Password secret can be used for these settings: FTP and SFTP username and password, the SFTP private key password, email username and password, the compression (Zip) password, the password for a log file sent by email, backup email username and password, network username and password, and cloud username and password. SSE-C cloud encryption keys count as passwords.
A connection cannot be deleted while a secret uses it, and a secret cannot be deleted while a profile uses it. Deleting a secret in SyncBackPro does not delete anything in 1Password.
Which 1Password items can be used
Only items in the Login and Password categories are listed, and only their username and password fields are used. Items in other categories are ignored.
That means an SFTP private key cannot come from 1Password. If you authenticate to an SFTP server with a key, keep the key in another supported secrets manager, such as Bitwarden or one of those described in the Secrets Manager article.
A connection covers one vault. If your backup credentials are in several vaults, create a connection for each, and give the token access to each vault.
Item titles matter
SyncBackPro finds a 1Password item by its title and nothing else. The title must match exactly, including upper and lower case. This has two consequences you should know about before you start.
First, if you rename an item in 1Password, every profile that uses it fails with Secret does not exist until you modify the secret in SyncBackPro and select the item again under its new title.
Second, and more serious, if you later give a different item the old title, SyncBackPro will use that item from then on without any warning. So once a profile uses an item, do not rename it and do not reuse its old title. Give every item in the vault a unique title. If two Login or Password items share a title, SyncBackPro refuses to use either of them, with an error, rather than guess: 1Password lists items in no fixed order, so the username and password could otherwise come from different items.
Security
The 1Password approach has one clear advantage over the others: SyncBackPro never holds a master password or anything that could open your whole 1Password account. It holds an access token that works only against your own Connect server, and only for the vaults you chose.
- The token is stored encrypted in the SyncBackPro program settings, in the same way as the details of any other connection.
- The token works for anything that can reach the Connect server. Treat it as a password, and limit which machines can reach the server, for example with a firewall rule.
- Connect uses plain HTTP by default. On anything other than a trusted network, configure the Connect server with its own TLS certificate (the OP_TLS_CERT_FILE and OP_TLS_KEY_FILE settings, after which it serves HTTPS on port 8443 by default), or put it behind a reverse proxy that provides HTTPS. Then use the https:// address in SyncBackPro.
- Give the token access only to the SyncBack vault. Revoking the token in 1Password stops SyncBackPro retrieving secrets immediately.
- Keep 1password-credentials.json safe. It is how the Connect server itself signs in to 1Password.
- With 1Password Business, the Item Usage Report for the Connect server shows which items it accessed, and when.
On the SyncBackPro side, the value of a secret, including a username, is never stored and never shown on screen. The profile holds a hidden reference to the secret, much like a variable, and exporting a profile does not give whoever imports it access to the secret. SyncBackPro only reads from 1Password. It never creates, changes or deletes items.
Scheduled and unattended runs
Nothing on the SyncBackPro side depends on a logged-on user. Retrieving a secret is a plain HTTP or HTTPS request carrying the token, so it works the same when a profile is run elevated, under Windows Administrator Protection, from a scheduled task, or as another user. That account needs to be able to reach the Connect server, which matters if your firewall rules are per user or per program.
The real risk for unattended profiles is token expiry. When the token you created in step 2 expires, every profile using it fails, and a profile that runs at 2am will not tell you until you read its log or get its failure notification. Choose the expiry deliberately, put the renewal date in your calendar, and when the time comes create a new token and modify the connection.
Limitations
- A 1Password Connect server is required. Service accounts, the SDKs and the 1Password CLI are not supported.
- Only Login and Password items, and only their username and password fields, can be used. Private keys cannot come from 1Password.
- One connection covers one vault.
- Read only. SyncBackPro cannot add or update items in 1Password.
- Items are found by title only, so renaming an item breaks the profiles that use it.
Troubleshooting
| Symptom | Cause and fix |
|---|---|
| HTTP/1.1 401 Unauthorized: Invalid bearer token | The token is wrong, has expired, has been revoked, or belongs to a different Connect server. |
| HTTP/1.1 403 Forbidden: Authorization: token does not have access to vault ... | The token has not been given access to that vault, or the vault ID is wrong. |
| HTTP/1.1 400 Bad Request: Invalid Vault UUID | The Vault setting holds the vault's name, or something else that is not a vault ID. Use the ID from step 5. |
| HTTP/1.1 404 Not Found | The URL is wrong, for example /v1 has been included in it. |
| No secrets are listed, or No secrets found | The vault contains no Login or Password items. |
| Socket Error # 10061 Connection refused, Socket Error # 11001 Host not found or another socket error | SyncBackPro could not reach the Connect server. Check the host name and port, that the server is running, and that the computer, and the account the profile runs as, can reach it. Try the test in step 4 from the same computer. |
| More than one 1Password item is called ... | Two Login or Password items have the same title, even if one is a Login and the other a Password. Rename one of them so every title is unique, then, if needed, modify the secret in SyncBackPro and select the item again. |
| Secret does not exist | The item has been renamed, deleted or moved out of the vault, or the token can no longer see it. Modify the secret and select the item again. |
| It worked, then stopped working | The access token has probably expired. Create a new token in 1Password and modify the connection to use it. |
Bitwarden, Dashlane or 1Password?
If you already use one of these password managers, use that one. If you are choosing, these are the differences that matter for backups:
| Bitwarden | Dashlane | 1Password | |
|---|---|---|---|
| SyncBackPro talks to | The Bitwarden CLI on the same computer | The Dashlane CLI on the same computer | Your own Connect server |
| Plan needed | Any, including the free plan | Any (the Secrets item type needs a business plan) | Individual, Teams or Business (Connect is included at no extra cost) |
| What SyncBackPro stores (encrypted) | API key and master password | Device keys, which contain the master password | An access token for your Connect server |
| Proxy server | Yes, through HTTPS_PROXY | No, needs direct Internet access | Not needed if the server is on your network |
| SFTP private keys | Yes (SSH key items or secure notes) | Yes (secure notes or secrets) | No |
| Beyond username and password | Custom fields, secure notes, SSH keys | Email, secure notes, secrets | Nothing |
Conclusion
1Password takes more setting up than Bitwarden or Dashlane, because you have to run a Connect server. In return, access to your credentials stays on your own network, SyncBackPro holds only a revocable token rather than a master password, and you choose exactly which vault it can see. If you already run Docker somewhere on your network, the server is a short job. Keep the vault small, protect the token, and diarise its expiry date.
Further reading: